Security and privacy
Control you can prove.
staffplane is built for companies that ask questions before they start. This page says how the platform protects your data, leaves the last word to people and makes every step provable.
Separation
Every customer in a Space of its own
An isolated environment per customer
Every Space works in an isolated environment of its own, with its own resource quota and network rules that block everything not explicitly allowed.
Isolation levels
Standard, secure and high-secure: the higher the level, the more strongly an agent is shielded from the rest of the platform.
Credentials stay hidden
Credentials are stored once and never shown again. For repositories every run gets a token of its own that expires with it.
Data
What models see – and what they don't
EU models by default
A new Space uses models hosted in the EU, and the platform enforces this on every call. A reseller can lock this default for its customers.
Pseudonymisation before every model call
Names, contact details and further personal details in messages are replaced by placeholders before a model sees them, and put back into the answer.
Retention by your rules
You set per mailbox how long mail contents and attachments stay; then the platform deletes them.
Documents without storage
Through the API the platform reads the text out of documents without storing the file or the text, and holds back risky file types.
Control
People keep the last word
Shadow mode
The agent answers silently beside your team and sends nothing. Tools that would change something run as a dry run.
Post-hoc review
A person rates finished conversations of a live agent afterwards – all of them or a sample – with a score, a comment and a better answer.
Four-eyes approval
Process steps, work results and first mails to new contacts need two different people if you want. A service account never counts as the second pair of eyes.
Kill switch
One click stops every agent of a Space and of the Spaces below it, including running tool calls and answers.
Traceability
One audit trail for every path – without contents
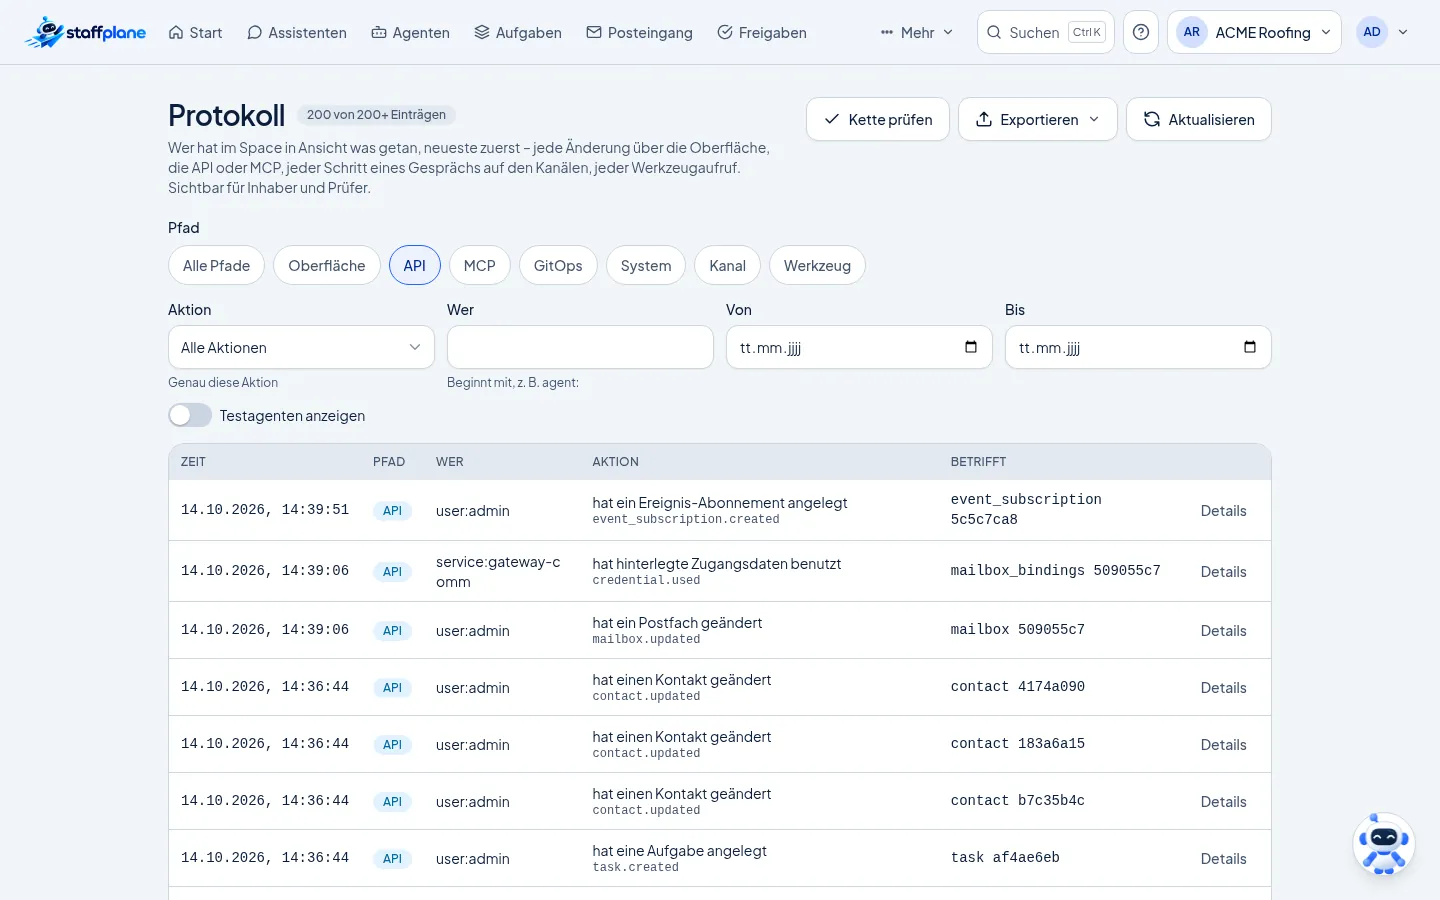
Every change through the interface, the API, MCP or GitOps, every step of a conversation on the channels and every tool call writes an entry: who, when, what, along which path. Message texts, values of tool calls and credentials are deliberately not in it.
The entries of a Space are chained with SHA-256; "verify chain" shows whether anything was changed afterwards. The trail exports as CSV or in the OCSF format, and streams to your SIEM as well – as a signed webhook or to Splunk.
The audit trail is open to a Space's owners and auditors.
Privacy
Tools for your duties under the GDPR
Access and erasure
Requests under Art. 15 and Art. 17 GDPR as a procedure: access as a ZIP, erasure under the four-eyes principle, a legal hold where a retention duty applies.
Records of processing
From a Space's configuration the platform generates a draft of the records of processing activities, as Markdown or PDF. The controller reviews and completes it.
Contacts from mailboxes
People who wrote to a mailbox or on WhatsApp can be included in access and erasure by their address or number as well.
Contract documents with versions
A Space's acceptance of the data processing agreement, the acceptable use policy and the privacy notice is recorded with version and time. The list of subprocessors follows its configuration.
AI notice
In the web chat, the notice that an AI agent answers appears before the first message. First WhatsApp contacts use only templates whose AI notice was confirmed.
Operations
Where and how the platform runs
Servers in Germany
The platform runs on servers in Germany that we operate ourselves.
On your own infrastructure
If you want, the same platform also runs on your own infrastructure – as an installation that belongs to your company alone.
Sign-in through your identity provider
Microsoft Entra ID, Okta or any provider with OIDC or SAML 2.0; users can be managed through SCIM.
Reviewed connections
Every MCP server in the catalog says who runs it and whether we reviewed its code. If a server changes a tool's description, the platform holds the tool back until a person agrees.
Your review
Ask us – we will show you
Send us your questionnaire on security and privacy: we answer it specifically and show you every safeguard in the running platform.
The data processing agreement, the acceptable use policy, the privacy notice and the list of subprocessors are ready; every Space's acceptance is recorded with version and time.
Have your requirements checked.
Send us your questions about security and privacy. We answer them specifically.